The facts
GSA uses Google Workspace to collaborate across the agency, and its Google Drive holds 2.5 million documents stored by GSA users and contractors. Some of those documents contain controlled unclassified information, material that is not classified but still requires protection from people without a legitimate business need to know.
During a limited search, the inspector general found 116 files containing that information that were improperly shared with all GSA users, exposing them to employees and contractors who did not have a legitimate business need to know. The exposed files included site plans in Washington, D.C. identifying site entrances, badge holder and visitor routes, screening areas, and screening techniques; a progressive collapse analysis describing collapse vulnerabilities, defense vulnerabilities, and critical failure locations; and a presentation with floor plans showing gun lockers, judges' chambers, jury rooms, metal detectors, and x-ray screening areas. The exposed personally identifiable information included social security numbers, dates of birth, phone numbers, and addresses, and the exposed business information included proprietary research and vendor proposals with technical and pricing information.
GSA did not detect the exposure because of deficiencies in its data loss prevention tool. The inspector general found GSA had not fully completed annual reviews of the tool's search terms, searches using the tool did not detect exposed documents that included current search terms, GSA had not incorporated many relevant terms from the agency's guidance into the tool's search terms, GSA had not implemented the available optical character recognition feature, GSA was unaware of the tool's file size limitation of 15 megabytes, and GSA had not documented program decisions affecting protection in Google Drive. The inspector general also found GSA lacks an approval process for properly sharing sensitive information and a standard naming convention that could more effectively prevent exposures.
This was not the first warning. The inspector general first reported in August 2014 that GSA did not protect sensitive information on child care centers, courthouses, water sources, building automation systems, and security and fire alarm systems in its Google cloud environment, issued additional reports between 2015 and 2017, and in April 2025 again identified unauthorized exposures, including safety surveys showing detailed blueprints, a site development plan in Washington, D.C., and a vendor's full bank account number and wire transfer information. The inspector general recommended restricting access for the 116 documents, identifying and notifying affected individuals, and improving the tool's management, and GSA's Chief Information Officer agreed with the recommendations.
Our take
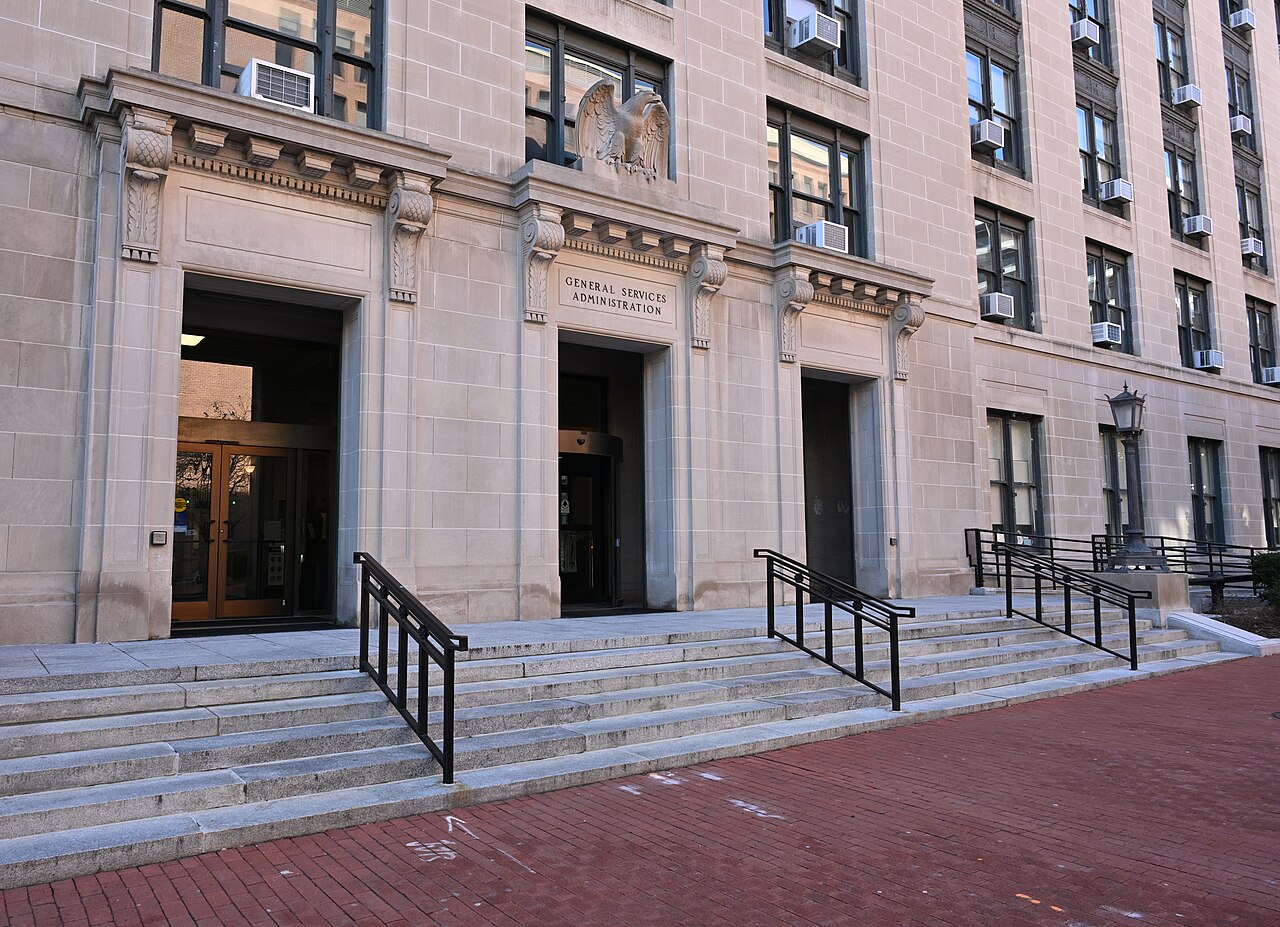
The General Services Administration, the federal dickheads in charge of securing government buildings, have been running the world’s most pathetic open house for over a decade. They didn’t need a hacker. They just needed a functioning brain cell, which was apparently too much to ask. They took 2.5 million documents, stuffed them into a Google Drive, and then, with the bureaucratic equivalent of a shrug and a fart, shared the whole fucking thing with every employee and contractor in the agency. The master keys to the kingdom were in a folder marked ‘For Everyone,’ and these useless pricks never noticed.
What was in this all-staff picnic basket? Oh, just the complete fucking blueprint for compromising federal security. Site plans showing visitor routes and screening techniques. Floor plans pointing out gun lockers, judges' chambers, and jury rooms. A goddamn ‘progressive collapse analysis’ detailing how to make buildings fall down. And, as a special treat for identity thieves, a buffet of Social Security numbers, birth dates, phone numbers, and home addresses. They even threw in a vendor’s full bank account and wire details, because why the fuck not?
The tool meant to stop this, their ‘data loss prevention’ system, was a joke they forgot the punchline to. They never finished reviewing its search terms. They never turned on the text recognition feature. They were blissfully unaware it just ignored any file bigger than 15 megabytes. It’s like buying a security camera, leaving the lens cap on, forgetting to plug it in, and then being shocked when you get robbed. The inspector general has been telling these assholes this exact shit since 2014. They got reports in 2014, 2015, 2017, and again in fucking 2025. Each time, the GSA’s Chief Information Officer nods along, says ‘yep, we agree,’ and then goes back to diddling the ‘off’ switch on their million-dollar useless toy.
This isn’t a security failure. It’s a monument to negligent, staggering incompetence. The agency tasked with protecting physical government infrastructure couldn’t protect a PDF in a shared drive. Their idea of ‘controlled unclassified information’ is to control fuck-all and classify themselves as absolute cunts. Every building plan they exposed is now a liability because the people guarding the fort left the drawbridge down and the portcullis up for eleven years. The only thing their ‘prevention tool’ successfully prevented was anyone at GSA giving a single shit.